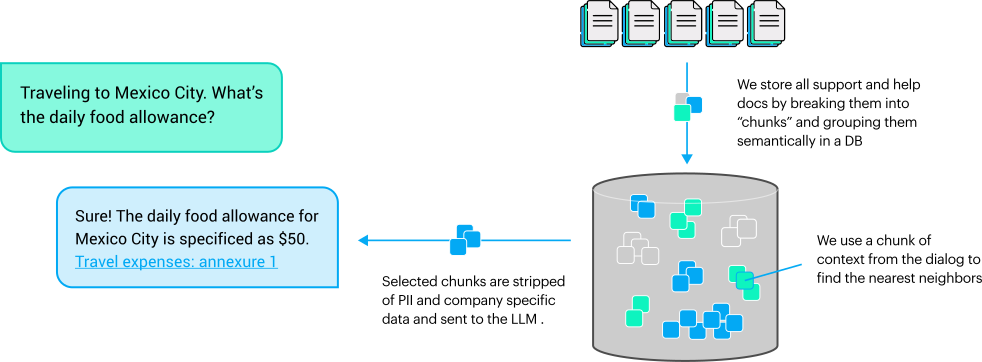
Achieving trustworthy AI is core to LLaMB™. Our natively built “Trust Layer” allows enterprises to deploy generative AI without compromising their security, compliance, or customer data.
One of the key challenges in the adoption of generative AI in the enterprise is security, compliance and ensuring the accuracy and authenticity of responses. Raw model APIs piped directly into the enterprise are very vulnerable. Moreover, these models are subject to adversarial attacks such as prompt injection. By carefully or maliciously crafting prompts, one can “lure” the models into giving unintended responses and influence their behavior.
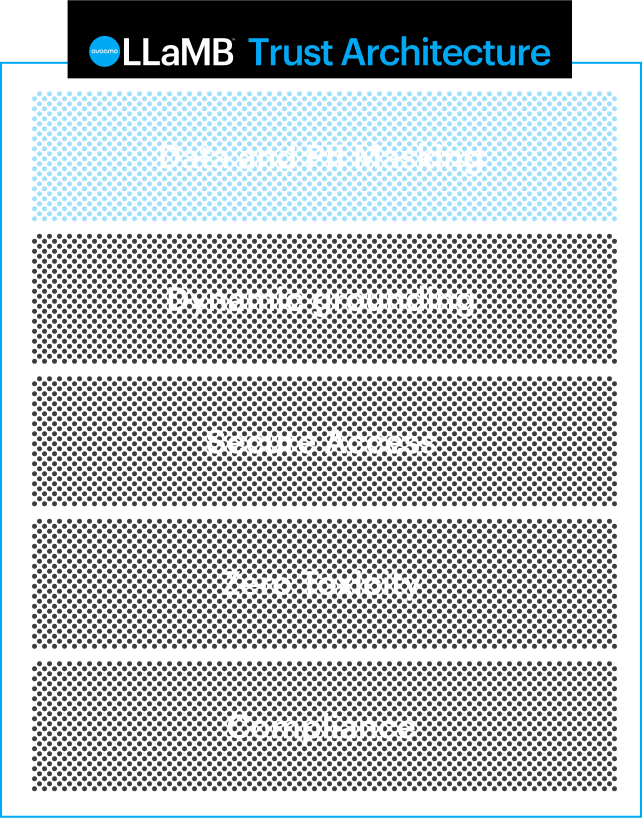
Avaamo LLaMB’s Trust Layer is an AI security-first architecture designed from the ground up so enterprises can solve these challenges and create a foundational trust layer for LLM applications.
Data and PII masking: Secures sensitive data by masking personal information in prompts. Automatically detects PII and payment data and redacts it from the prompt.
Dynamic grounding: Avaamo’s prebuilt prompts are grounded in enterprise data and are specifically fine-tuned not to use any public data.
Secure access: Enterprise identity, which defines who gets access to what data, is critical. Avaamo’s built-in access control ensures enterprise access policies are applied, so responses are accurate and personalized, and users can only perform actions they are authorized to perform.
Zero toxicity: Avaamo ensures zero toxicity by making the LLM not only domain aware but aware of your company, so it can act as an ambassador for your company and protect your brand.
Compliance: LLaMB is fully GDPR, CCPA, SOC 2 and SOC 3 compliant out of the box.